Guide
Global Control, EU Compliance: How to Stop Choosing Between Efficiency and Rules
Introduction
Managing global governance, risk, and compliance (GRC) used to be a balancing act between corporate strategy and local market needs. Today, it feels more like walking a tightrope in a legal crosswind.
When global headquarters demand centralised efficiency and local EU subsidiaries face strict national penalties, operational friction is inevitable. Here’s how enterprise GRC teams can establish an agile, centralised system of record that harmonizes global standards with complex localised European mandates.
The operational friction of overlapping European regulations
For European GRC leaders, the regulatory landscape has entered an era of aggressive enforcement. The Digital Operational Resilience Act (DORA) has been directly applicable across financial entities since January 2025. Simultaneously, the NIS2 Directive has been transposed into national law across EU member states — bringing thousands of previously unregulated entities under strict cybersecurity supervision.
DORA
DORA is a direct-application EU Regulation targeted specifically at the financial sector and its ICT vendors.
NIS2
NIS2 is an EU Directive covering a broader range of critical sectors that requires individual transposition into national law by each member state.
The primary driver of regulatory friction in the EU is the conflict between centralised global efficiency and localised legal liability. While global GRC teams strive for unified, single-source-of-truth repositories, European operations must navigate local legal nuances:
Architecting a common controls framework
Trying to manage DORA, NIS2, ISO 27001, and SOC 2® through isolated point solutions creates exponential control redundancy and audit fatigue.
To combat these challenges, organisations can use native framework crosswalks to “map once, comply everywhere.” Centralising core operational controls — such as multi-factor authentication (MFA), encryption, patch management, and business continuity — allows a single control to satisfy multiple global and regional requirements simultaneously.
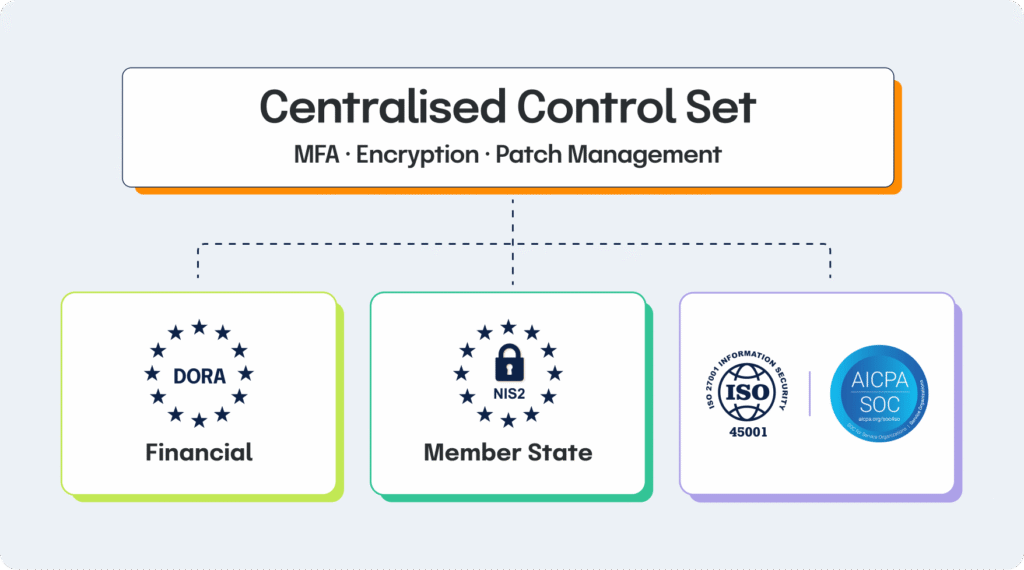
Transitioning from siloed frameworks to a standardised common control set reduces duplicative controls by up to 66% and saves over 350 hours on annual audit preparation.
Operationalising distributed ownership with hierarchical scopes
To balance central visibility with local accountability, your GRC tech stack must mirror your operational corporate reality.
Global governance fails when local managers feel compliance is something “done to them” by remote executives. To resolve this, organisations can use Hierarchical Scopes, a structural model that segments compliance programs up to 10 levels deep (e.g., Global Org ->Region -> Entity -> Local Product).
This model allows local entity managers in Germany or France to own their specific compliance outcomes and customise controls for national transpositions. Simultaneously, live telemetry rolls up to the corporate GRC team, delivering real-time enterprise visibility without stripping autonomy from local business units.
Operationalising distributed ownership with hierarchical scopes
Third-party risk management in the EU has shifted from periodic vendor questionnaires to automated, continuous posture monitoring.
Under DORA Chapter V and NIS2 Article 21, financial and essential entities face strict third-party oversight obligations. DORA specifically requires financial entities to maintain and submit a highly prescriptive Register of Information covering all ICT third-party service providers.
To meet these demands, GRC teams must:
1 Centralise vendor security documentation (SOC 2 reports, penetration tests, and custom questionnaires) into a single auditable repository.
2 Utilize AI-powered third-party risk management (TPRM) to automatically ingest, extract, and analyse vendor evidence in minutes rather than weeks.
3 Continuously monitor external security posture to detect systemic supply chain concentration risks and vulnerabilities before regulators do.
Integrating risk management across borders
Local control failures should automatically update corporate risk posture in real time.
A failed backup test in an EU subsidiary shouldn’t wait for a quarterly board deck to be noticed. By connecting operational control health directly to unified risk registers, organisations protect themselves proactively.
When automated evidence ingestion detects a regional control failure, the corresponding risk score updates dynamically across both regional and global risk registers. Centralising issue remediation workflows across international engineering, legal, and security teams ensures that vulnerabilities are addressed before they escalate into breach notifications or regulatory fines.
Driving audit readiness and business growth
Transitioning away from manual spreadsheets and email tracking turns compliance from a costly administrative burden into a competitive growth advantage.
Manual compliance creates operational drag. By leveraging continuous evidence collection capabilities such as Hypersyncs, GRC teams keep both global frameworks and regional EU mandates audit-ready 365 days a year.
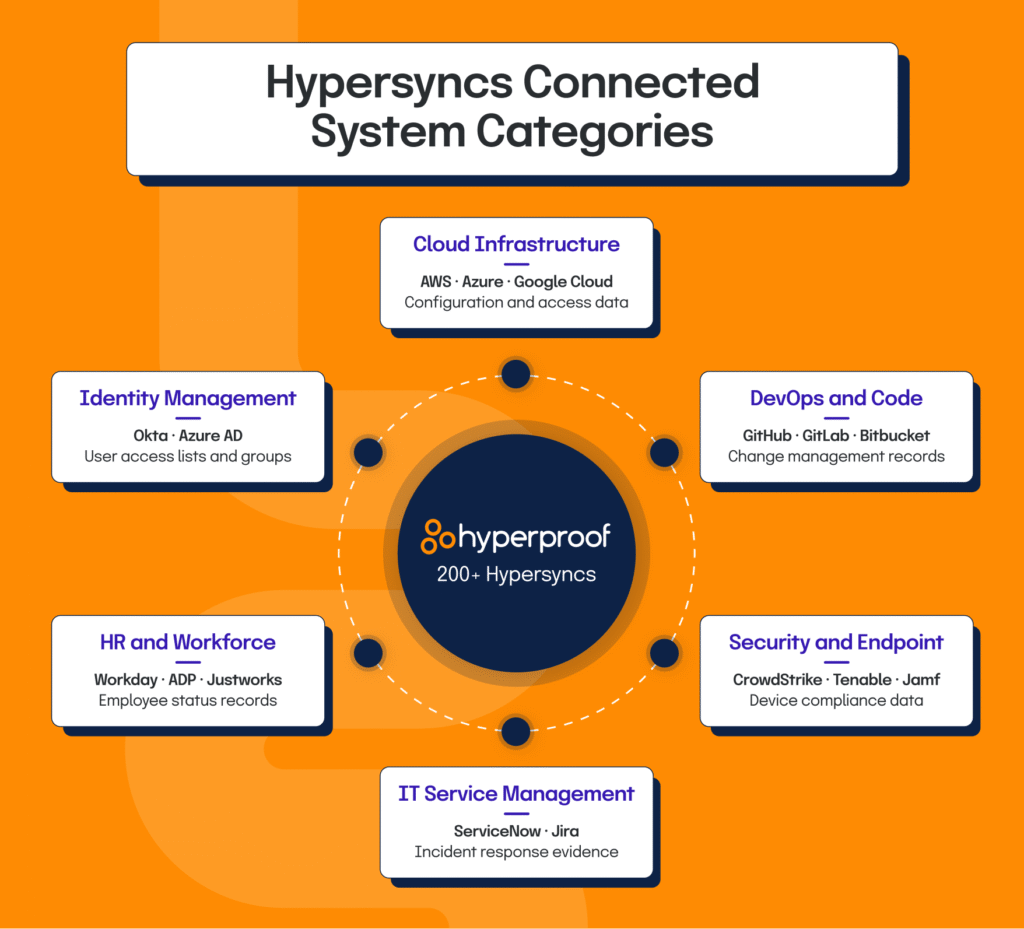
Generating consistent, defensible metrics on demand proves continuous control health to international auditors and supervisory authorities alike. Equally important, it accelerates deal cycles and market expansion across Europe.
Appian, a global process automation organisation, uses Hyperproof’s Scopes and Hypersyncs to ensure compliance with 28 frameworks, streamline evidence collection, and enable market expansion.
Reducing operational friction with Hyperproof
Prioritising architectural flexibility in your GRC tech stack is no longer optional for organisations expanding their footprint across Europe. By replacing fragmented point solutions with common control mapping, flexible scopes, and automated risk tracking, enterprise GRC teams achieve a rare triple win: reduced operational costs, faster market expansion, and unwavering stakeholder trust.
Contact us to see how Hyperproof can help your organisation reduce operational friction and balance global GRC goals with local mandates.