CISO for a day
Your Mission: Level Up Your GRC Maturity
You’ve got the title for the next 10 minutes. Congrats — and good luck. Your board wants answers, your auditor wants evidence, and your third-party vendor list just doubled. Every call you make either moves your program forward or adds it to next quarter’s incident report.
CISO for a Day is Hyperproof’s interactive take on the GRC maturity assessment you already know — except instead of answering 15 questions, you’re living out real scenarios. Make the calls a real compliance leader makes under real pressure, and find out where your organization actually stands.
What you get
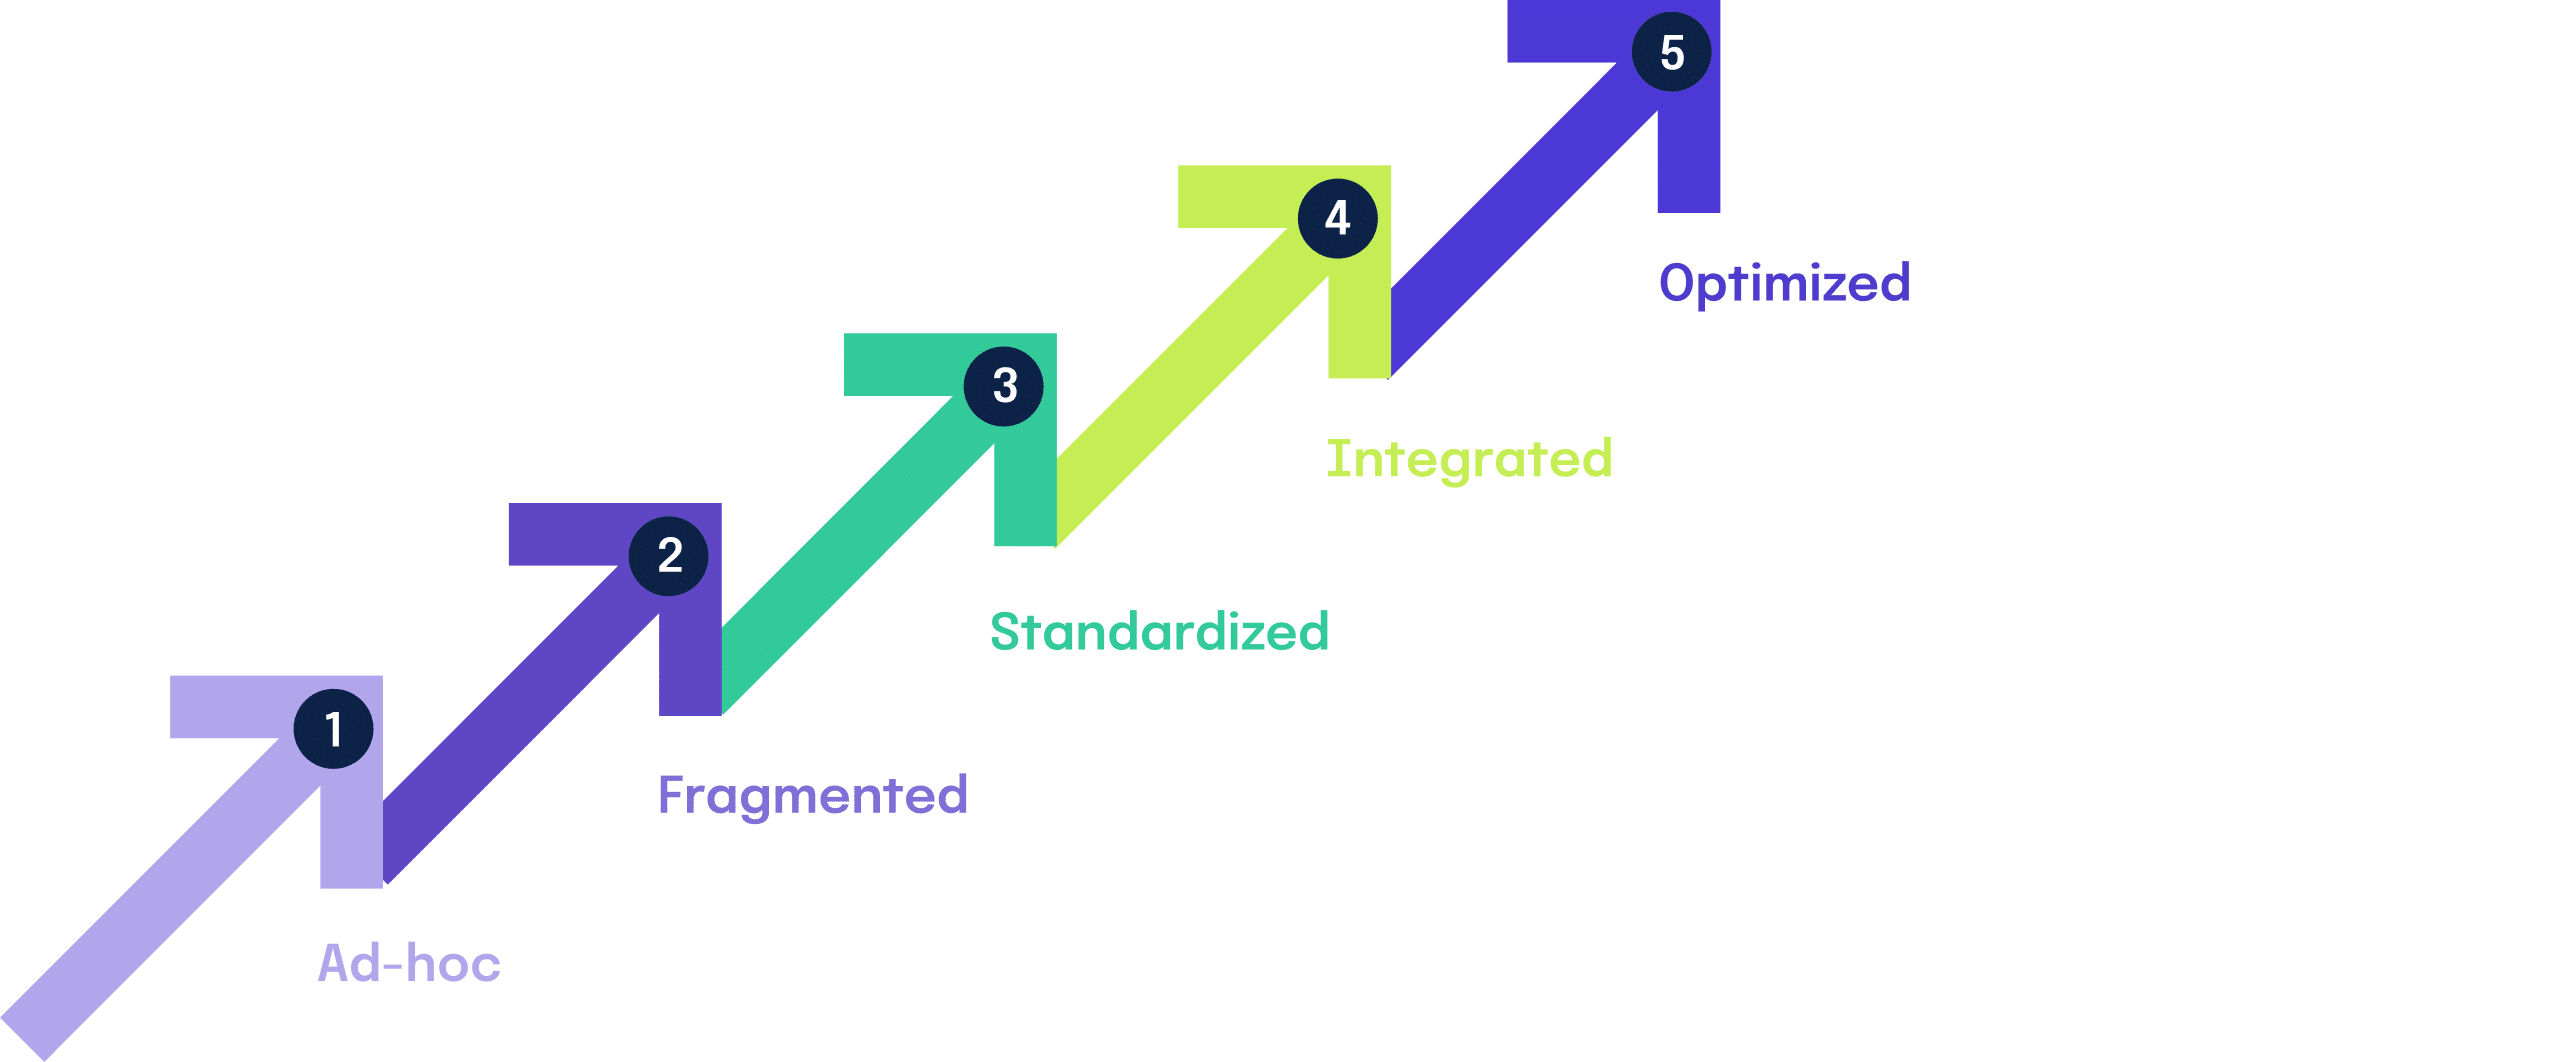
1 Your GRC maturity level: Mapped to Hyperproof’s 5-stage model, based on the decisions you made, not a self-reported guess
2 A CISO Report Card: Shareable breakdown of how you handled governance, risk, and compliance under pressure, plus where you left points on the table
3 A tailored roadmap: Specific next steps to move up a level, mapped to your actual weak spots
4 The option to go deeper: Book time with a Hyperproof GRC expert for a personalized assessment of your program
1.
Play through a day in the life of a CISO: Go through 9 scenarios
2.
Get your maturity result with the reasoning behind it
3.
Unlock your tailored roadmap on how to level up your GRC maturity
The GRC maturity levels
Where does your organization fall?

Success Story
How Acuity International improved their GRC maturity with Hyperproof
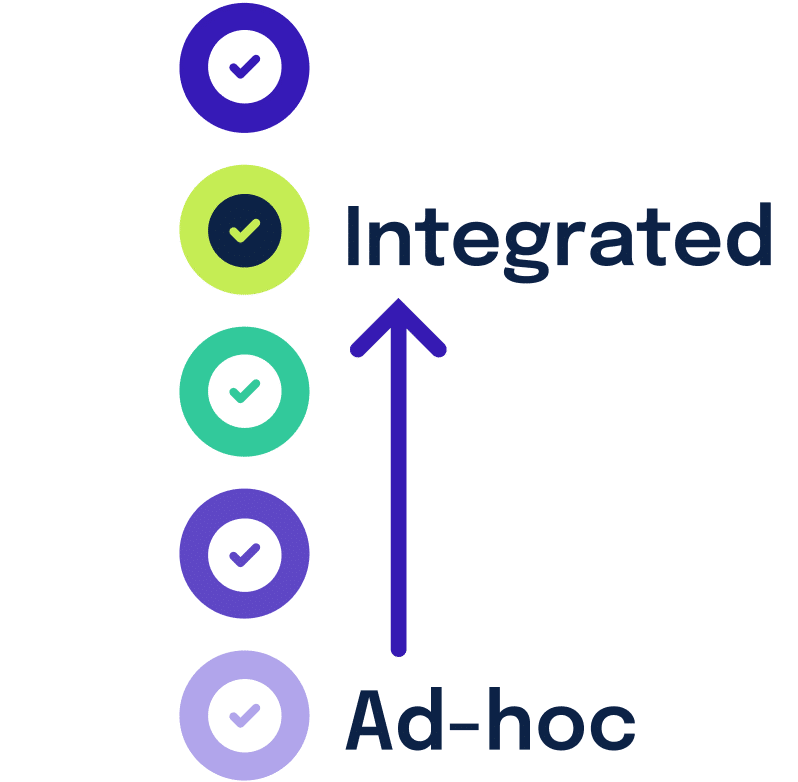
With Hyperproof, Acuity International has graduated from ad-hoc to integrated maturity. Their team now spends about 1/3 of the time on manual processes like managing governance packages and audits.
Level Up Your GRC Maturity
CISO for a Day turns the GRC maturity assessment into real scenarios. Make the calls. Find out where you actually stand.